Layer 7 WAF with IPDB: Auto-Block Real IPs Behind Cloudflare & Akamai
We’re rolling out one of our most powerful updates yet: next-gen Layer 7 WAF with IPDB protection for proxied traffic. Attackers hiding behind Cloudflare, Akamai, Fastly, or Nginx? Not anymore. Our latest update exposes the real source IP—even through multiple proxy layers—and blocks them instantly on auto-pilot.
No More Hiding Behind Proxies
This update introduces a proxy-aware WAF module that works at server level. It identifies the real client IP and stops malicious traffic—even if attackers are routing through trusted proxies. It’s automatic, fast, and smart.
Key Features:
- 20x Stronger Protection: By accurately detecting real IPs behind proxies, our new WAF now blocks a massive number of attacks that previously slipped through—stopping threats before they ever hit your server.
- Proxy-Aware Detection: Works seamlessly with Cloudflare, Akamai, Fastly, Nginx, and similar services. Real IPs get exposed and blocked instantly.
- Integrated with All Modules: Now fully tied into the Brute-Force and Log Analysis modules. Works just like Fail2ban—except faster, automatic, and backed by WAF power.
- Global Intelligence Sharing: Like CrowdSec, but built into cPFence. Over 4,000 servers now sync attack data. If one server detects a threat, it’s blocked across the entire network within hours.
- Lower Load, No Spikes: By filtering out malicious traffic early—especially from proxies—our new WAF offloads junk requests before they reach your apps, reducing server load and preventing resource spikes.
- Full IPv6 Support: Half of modern brute-force and DDoS attacks now come from IPv6. Unlike our competitors, cPFence handles IPv6 cleanly at the WAF & IPDB layer.
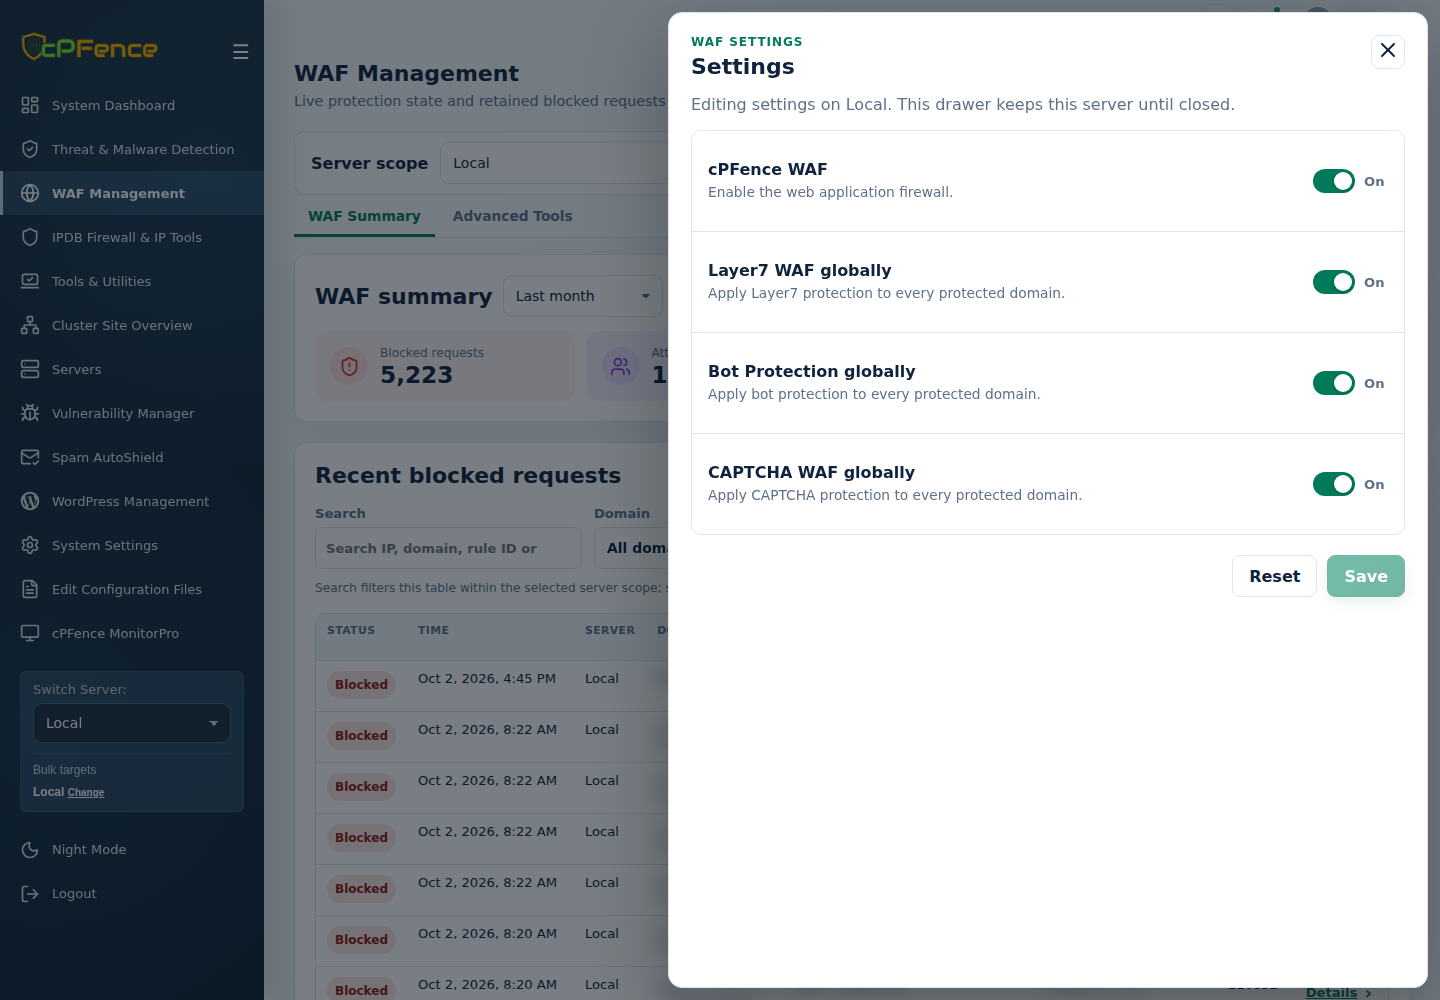
- Protection on Your Terms: Manage Layer 7 protection, bot protection and WAF CAPTCHA independently, with global and per-domain controls. The WAF master switch still needs to be on.
- Precise Exceptions: If a legitimate request hits a rule, make a narrow domain-and-rule exception instead of turning off protection for the entire server.
Still Relying on IPv4-Only Protection?
Here’s what you’re missing. Modern attacks are evolving—and they’re already using IPv6 at scale. In cPFence v4+, open IPDB Firewall & IP Tools → IPDB summary to inspect recorded blocked IPs. Use Search, Reason, Country and Last seen since, then Apply filters to narrow the selected server’s table:
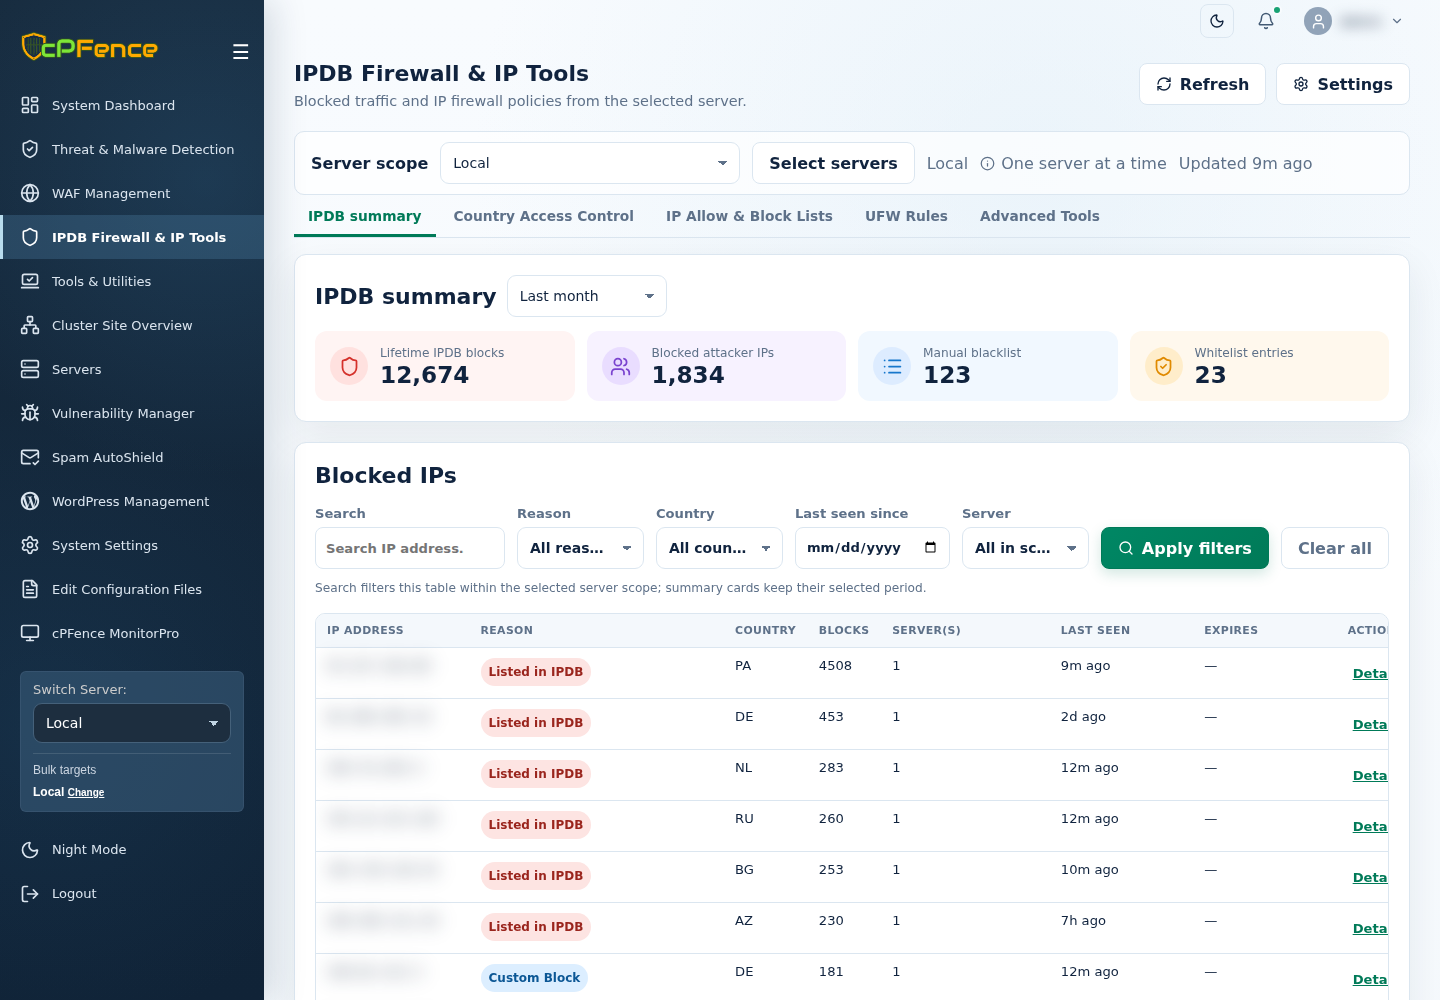
If your current WAF solution doesn’t support full IPv6 handling, you’re flying blind against half of today’s attackers.
See It in Action
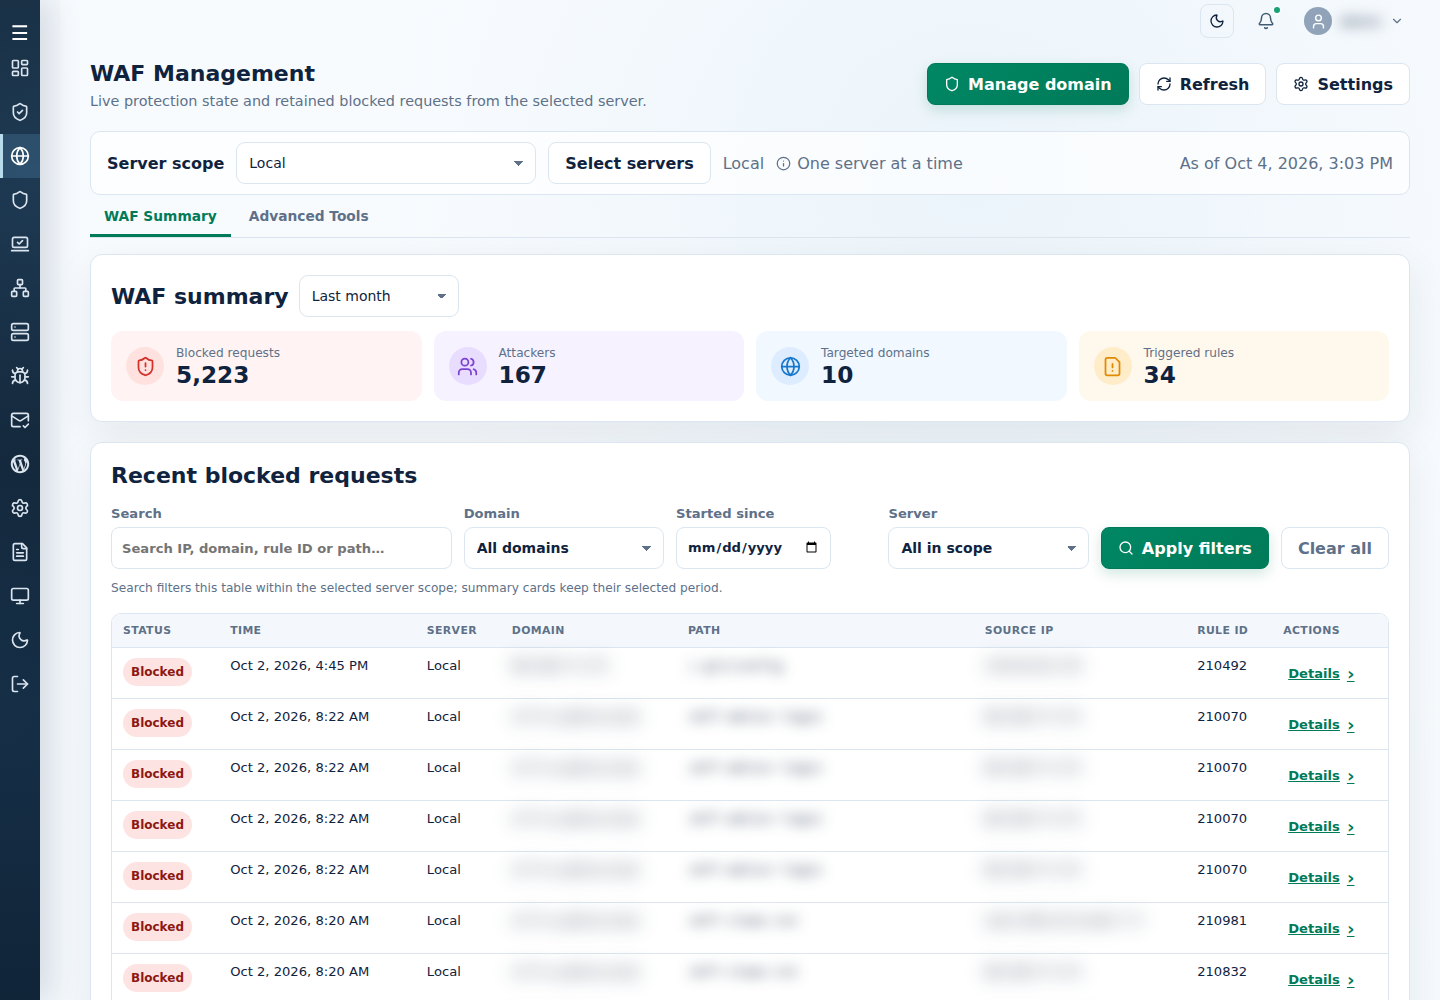
In cPFence v4+, open WAF Management, choose your server scope, and inspect WAF Summary → Recent blocked requests. Use the search, domain and time filters, then Apply filters; open a request’s Details to inspect its recorded source IP, rule and request information. Select Refresh to reload the retained view. You’ll notice a major difference in both visibility and performance.
Ready to tune the layers? Open WAF Management → Settings for the intended server to review the master and global switches. For one website, use Manage domain → Domain settings and review its Layer 7, bot and CAPTCHA choices before saving. WAF CAPTCHA is a hosted challenge, separate from WordPress’s math CAPTCHA; check login-page caching compatibility when using LiteSpeed Cache.
Prefer the terminal? As root on the server hosting the domain, replace example.com with your actual target:
cpfence --enable-layer7-waf-domain example.com
cpfence --enable-bot-protection-domain example.com
cpfence --enable-captcha-waf-domain example.com
For a confirmed false positive, use cpfence --disable-waf-domain-byid example.com RULE_ID with the actual matched rule ID. Restore that rule with cpfence --enable-waf-domain-byid example.com RULE_ID. Review the selected domain and verify legitimate requests afterward; see WAF rule exceptions.
Protect Your Enhance Cluster with Cloudflare: Full Guide Coming Soon
We’ll soon publish a full step-by-step guide on how to put your entire Enhance cluster behind Cloudflare on the cPFence Community. This, combined with our new proxy-aware WAF protection, will make your cluster virtually bulletproof in both performance and security.
Make sure to join our community at https://community.cpfence.app/ to stay updated with the latest tips, walkthroughs, and tools that keep your infrastructure secure, optimized, and always evolving.
Try It Free Today
Not using cPFence yet? This is the perfect time to see it in action and experience the difference on your servers.
Start free trial