Wp2shell Mitigation for WordPress
A critical vulnerability in WordPress Core, known as wp2shell, affects:
- WordPress 6.9.0–6.9.4
- WordPress 7.0.0–7.0.1
- WordPress 7.1 Beta 1
The official fixes are included in WordPress 6.9.5, 7.0.2, and 7.1 Beta 2. See the official WordPress security announcement.
For older WordPress installations that cannot be upgraded at the moment, cPFence has released a free standalone plugin that blocks the malformed REST API batch requests used by the vulnerability.
Download the plugin:
Save the file as:
cpfence-wp2shell-mitigation.php
Then upload it to:
wp-content/plugins/cpfence-wp2shell-mitigation/
Activate it from Plugins in WordPress.
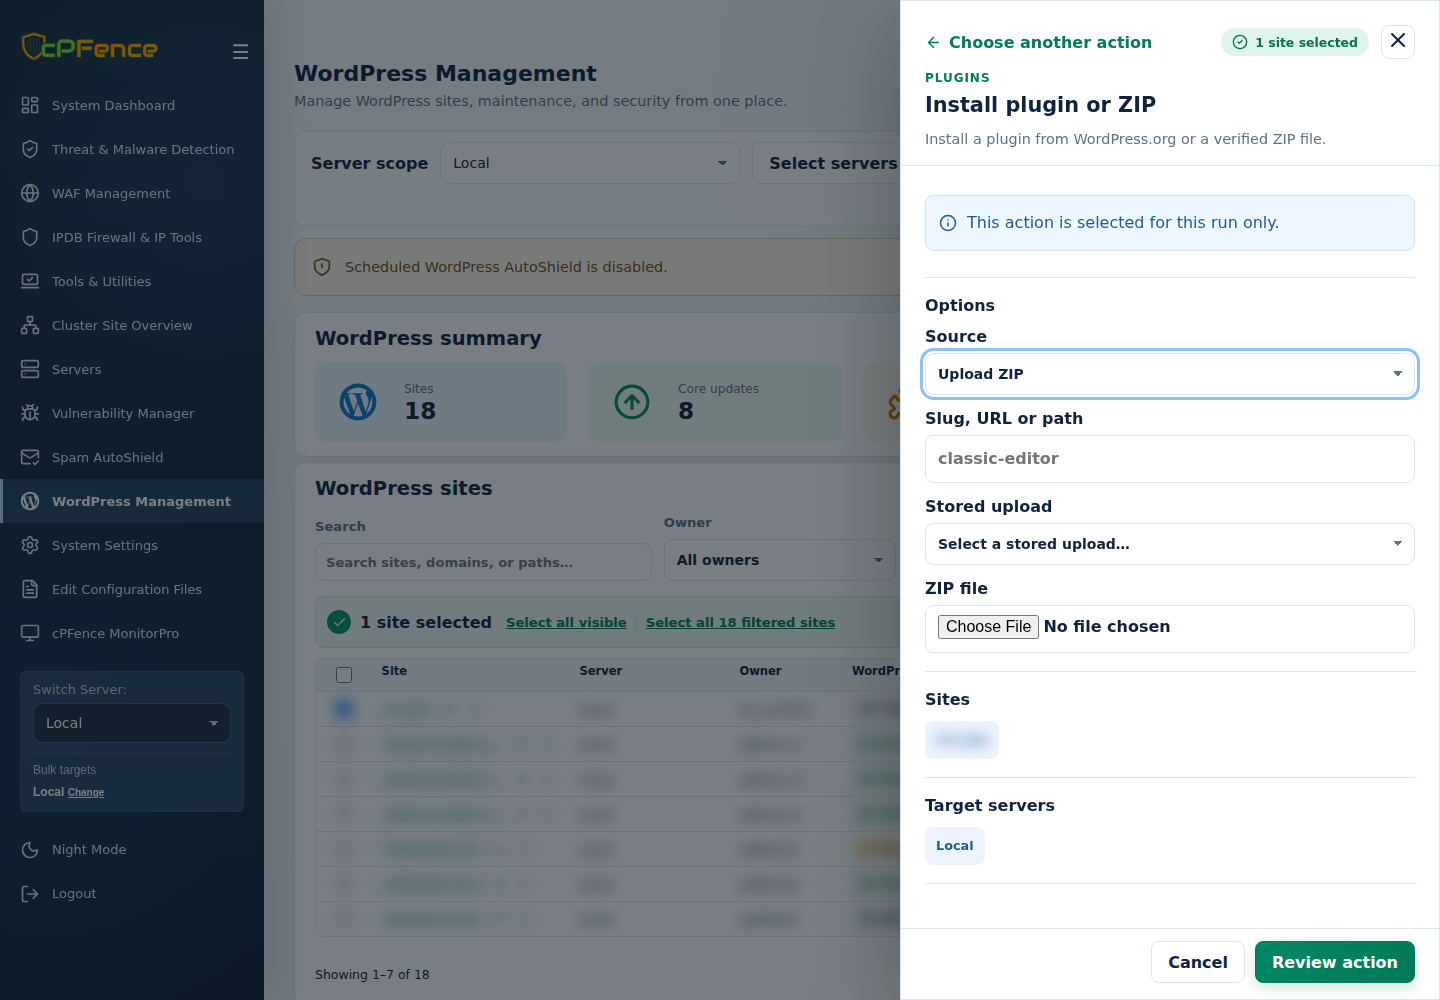
If you are using cPFence, you can deploy the plugin ZIP across selected or all websites on all servers using cPFence’s bulk plugin installation tools. Zip the plugin folder, then in cPFence v4+ open WordPress Management, choose the intended servers and sites, and use Choose action → Bulk tools → Plugins → Install plugin or ZIP. Choose Upload ZIP, select the package, and click Review action. Confirm the exact targets and read each site’s final result; uploading alone does not install it. Enable the plugin separately after installation:
More info:
How to install a WordPress plugin or ZIP with cPFence v4+. Keep a usable backup and test on one site first; installation can overwrite plugin files. These ordinary v4+ bulk tools do not require passwordless inter-server SSH.
This plugin is only a temporary mitigation. Update WordPress Core as soon as possible, then deactivate and remove the plugin.
DISCLAIMER
 ----------
This plugin is a temporary mitigation, not a replacement for the official
WordPress security update. Back up your site and test this plugin in a
staging environment before using it in production. It is provided "as is",
without warranty of any kind. Linkers Gate LLC and the cPFence.app Team are
not liable for site downtime, incompatibilities, data loss, security
incidents, or other damages arising from its use.
Keep WordPress protection within reach
Manage selected-site security tools and updates with cPFence v4+ for Enhance.
Start free trial