Missed Malware? We’ll Credit You $1
Found malware on your server that cPFence missed? Let us know. For every report we confirm, we add $1 to your account credit.
cPFence v4+ is our strongest protection yet, far beyond v3, and we’re confident enough in it to put money behind every miss.
Signatures you can rely on
cPFence signatures are among the strongest commercial malware detection signatures on the market, trusted by hosting providers for years. Our team runs dozens of honeypots that capture new threats as they appear, so detection gets stronger every day.
No detection system catches everything, and that’s where you come in. Every confirmed sample becomes a new signature that protects every cPFence server. You find it, we close the gap, and everyone benefits.
How to report missed malware
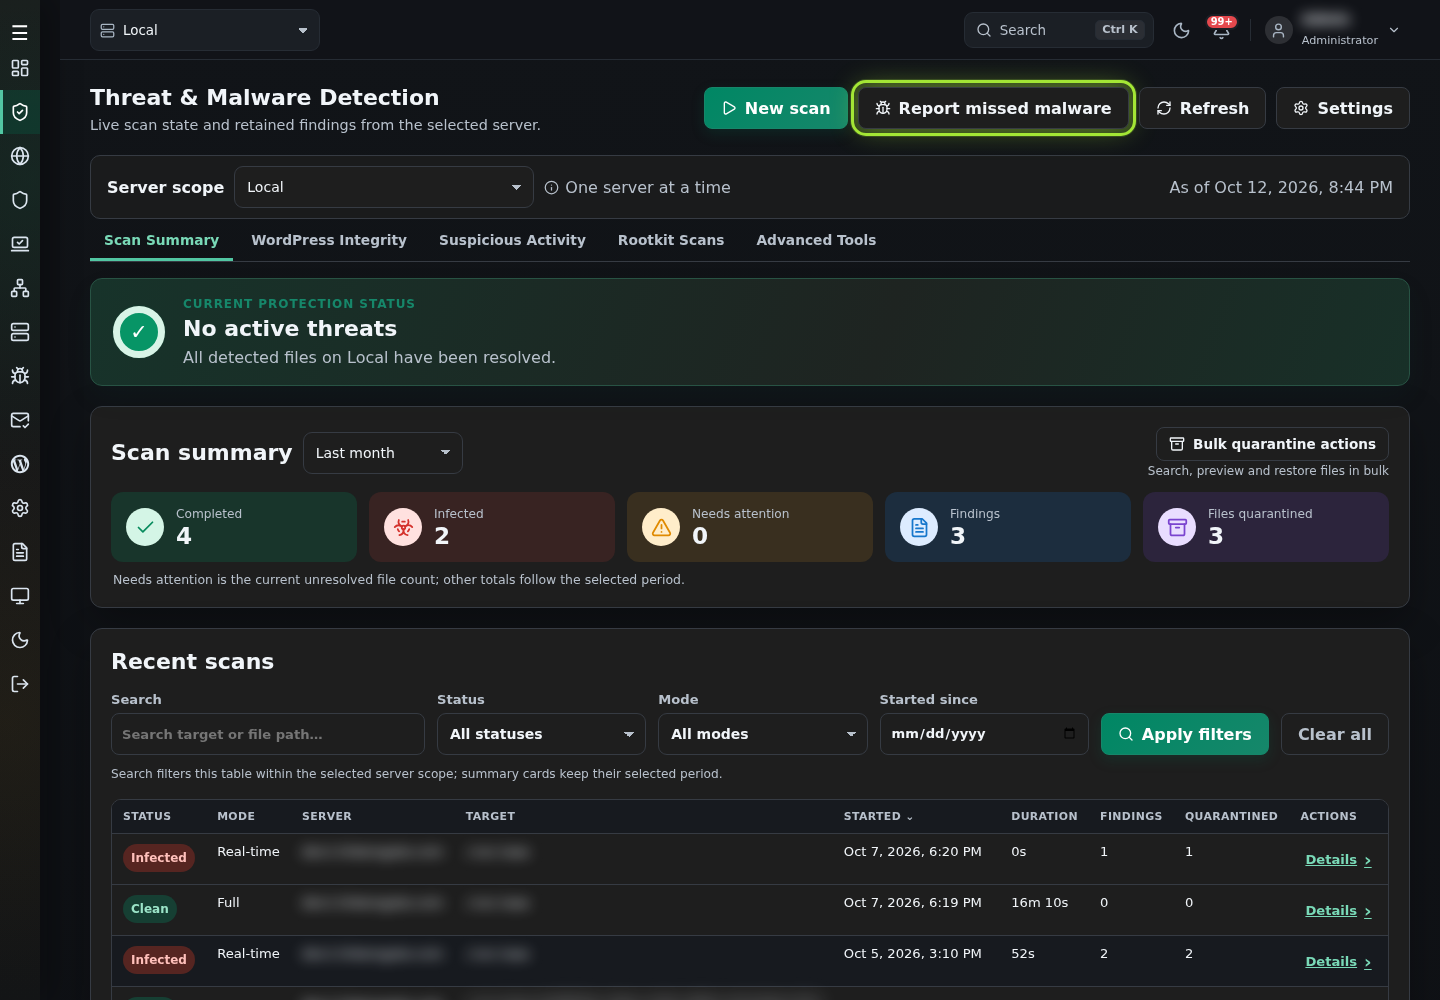
1. In the WebUI, open Threat & Malware Detection and select Report missed malware, next to New scan.
2. Choose the file and select Check and send. Upload the file itself, up to 5 MB, not a ZIP or a password-protected archive.
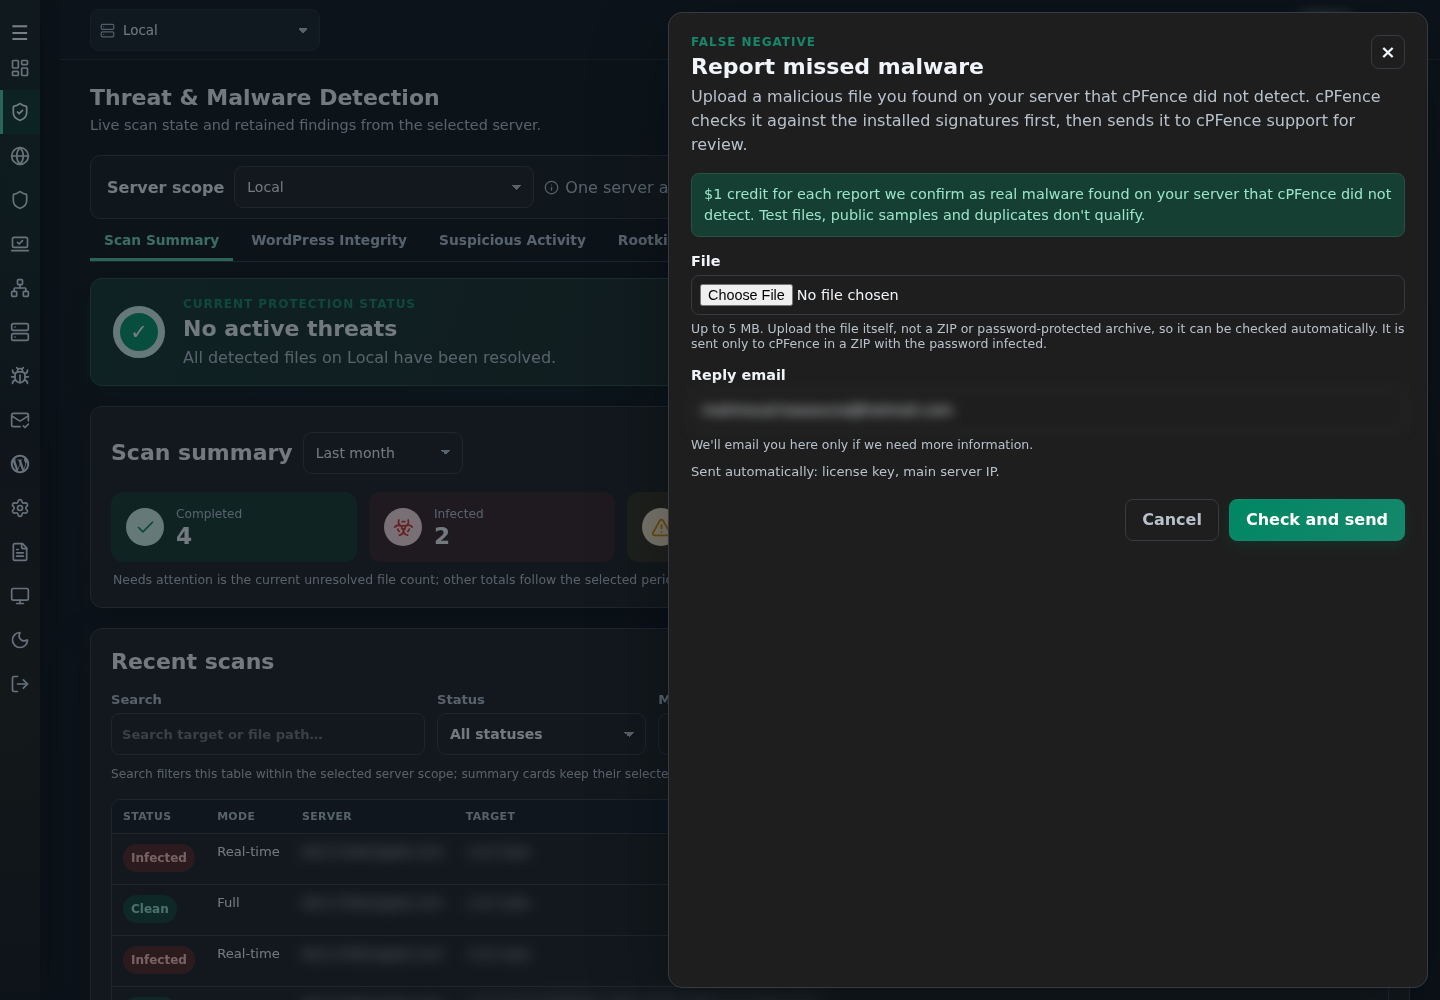
cPFence first checks the file against your installed signatures. If it’s already detected, you’ll know right away and nothing is sent. Otherwise, the file goes to our team with only your license key and main server IP.
How the $1 credit works
- $1 for every confirmed miss: real malware found on your server that cPFence did not detect.
- Real account credit: added to your account in the client area, to use toward your invoices.
- We let you know: we email you when the credit is applied.
- What doesn’t qualify: test files, public samples and duplicate reports.
Help us catch what we missed
Report missed malware is available in cPFence v4+, starting with the current release candidate. See report a false positive or missed malware in the docs.
Found something we missed? Send it our way.