Understand DDoS protection behind a proxy
When a site is behind Cloudflare or another reverse proxy, network connections to the origin can come from the proxy instead of the visitor. cPFence v4+ IPDB connection counts and WAF request inspection therefore have different inputs.
Check CDN access
Section titled “Check CDN access”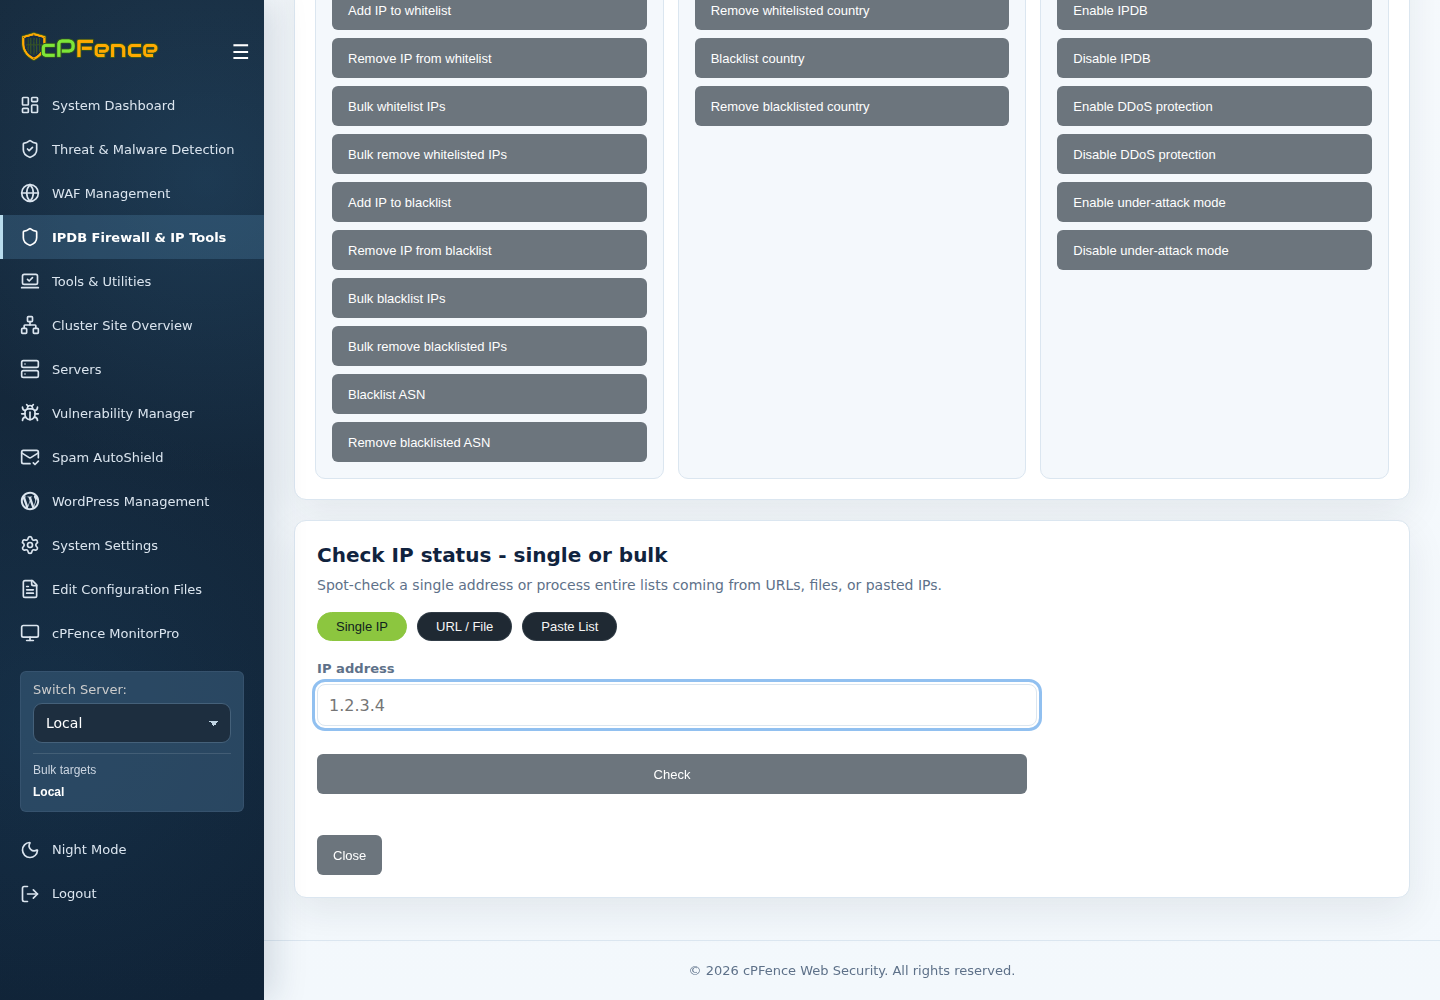
You can use cPFence alongside Cloudflare, Quic.Cloud, BunnyCDN, Gcore, CacheFly or Fastly. A CDN’s caching and edge protection can complement protection at your origin.
Use your own reverse proxy
Section titled “Use your own reverse proxy”There is no separate trusted-proxy setting. If your own proxy, such as nginx, sits in front of your servers:
- Whitelist the proxy’s IP addresses on every server, so the firewall and connection limit never block it.
- Keep the proxy overwriting the forwarded visitor-IP headers. The WAF then checks and blocks each visitor by their own IP; whitelisting the proxy does not exempt the visitors behind it.
- Accept web traffic on the servers only from your proxy and CDN.
Check visitor addresses
Section titled “Check visitor addresses”- Confirm that the web server trusts visitor-IP headers only from your configured proxy network.
- Check that access logs record the expected real visitor address.
- Compare the network peer, logged visitor IP and WAF event for the same request.
- Inspect the current proxy/whitelist policy before blaming a missing block on an inactive firewall.
See WAF engine limits and IP status. Configure edge protection with your proxy provider for attacks that do not reach the origin as distinct visitor connections.