
Trust or stop trusting a sender ASN
Open Spam AutoShield and choose the mail server whose policy you want to inspect. The master must be on for stored entries to take effect; see the illustrated Spam AutoShield guide.
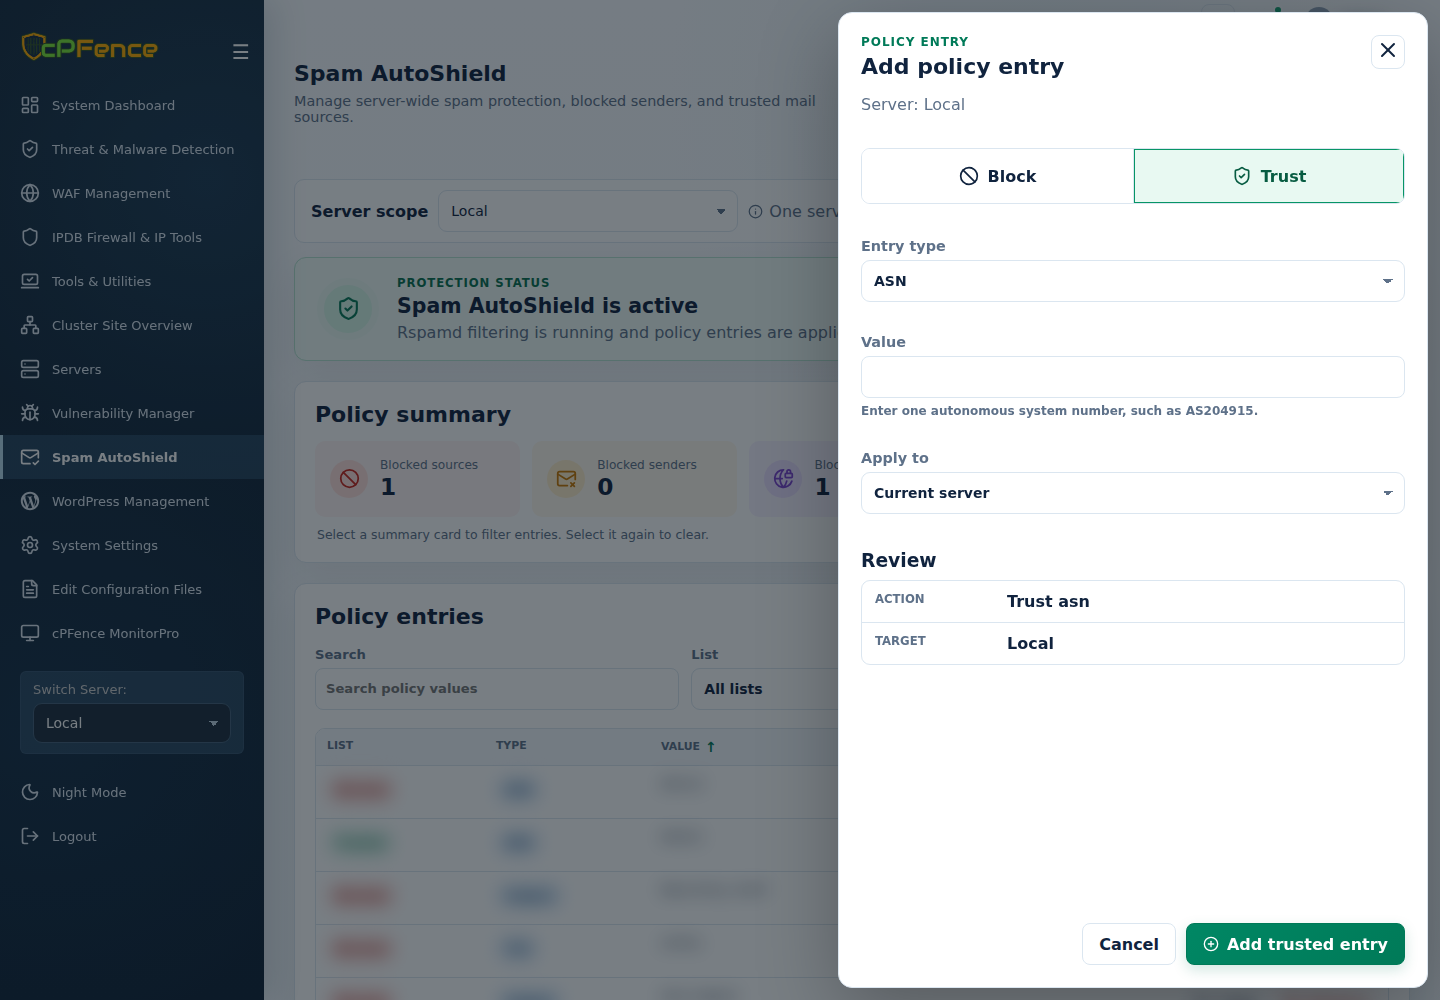
- Click Add entry and choose Trust.
- Set Entry type to ASN and enter an ASN such as
AS13335. - Choose Apply to, review the servers, then click Add trusted entry.
- Read every server’s result and refresh the intended list.
To remove the trust exception, filter List and Type, find the exact value, and use Remove on the displayed server. Review its confirmation and result.
Record why the network is trusted and review the exception regularly. Trust entries do not replace mail authentication.
Command-line method
Section titled “Command-line method”From a root terminal on the intended mail server, add a trusted sender network:
cpfence --add-spam-autoshield-wl-asn AS13335Remove that same trust exception:
cpfence --del-spam-autoshield-wl-asn AS13335Replace the example with the verified network you intend to trust. Both AS-prefixed and numeric ASN values are accepted. These commands update this mail server’s policy, not the WebUI’s Apply to selection. Read the result and refresh its ASN trust list.
Keep a record of why the ASN is trusted and review it regularly. Prefer a narrower sender-address exception when sufficient. The current trust rule requires passing SPF or DKIM; it does not guarantee delivery or remove separate blocks.